Search
Items tagged with: Security
Let’s Talk About Why all This OT Stuff is Connected
source: https://tisiphone.net/2026/11/08/lets-talk-about-why-all-this-ot-stuff-is-connected/
The next time a headline lands about hacked pumps or freezers, and you feel the urge to ask why they don’t just disconnect it, remember that there’s rarely a single plug left to pull. These connections were built one sensible business decision at a time, and they now help keep the lights on, the water running, and the food cold.
#hack #hacker #supermarket #food #infrastructure #criticism #security #cybersecurity #internet #online #future #iot #fail #news #analysis
Let’s Talk About Why all This OT Stuff is Connected
It’s been a really bad month (and year) for OT cybersecurity. From a wave of new, high-impact vulnerabilities, to attacks on supermarket refrigerators, to attacks on blood banks, we’ve …Lesley Carhart's Cybersecurity Blog

WriteFreely v0.17.3 is out now with some critical security patches.
We recommend ALL admins update their instances as soon as possible!
https://github.com/writefreely/writefreely/releases/tag/v0.17.3
#WriteFreely #releases #security
Release v0.17.3 · writefreely/writefreely
Our latest patch version contains several critical security fixes, including one for an authentication bypass that let unauthenticated attackers use the API as another user. It also fixes several o...GitHub
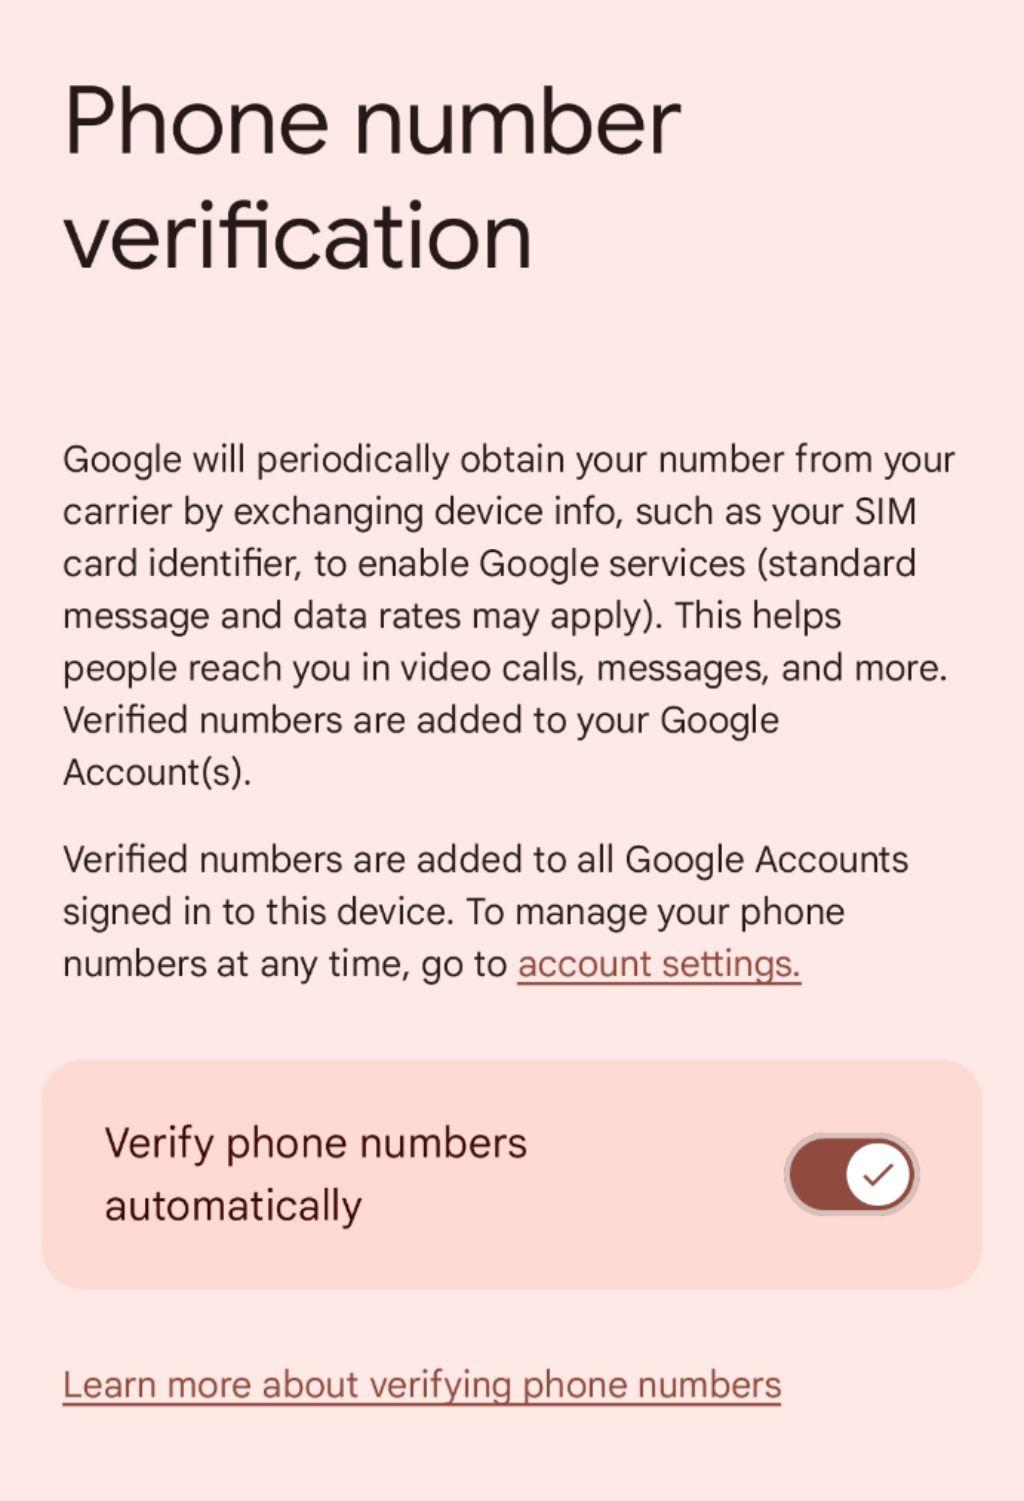
🚨 #Google is collecting phone numbers /SIM from your phone by default now without asking for consent, here is how to disable it
I have a test phone with stock Android (and hence Google services) to test how the apps I develop behave there etc.
The other day I woke up with a notification in that phone, out of the blue Google was telling me they "verified my phone number" basically they stole/collected my phone number from my phone and sent it to their servers without any consent.
I know the trust bar is very low, but even then I didn't expect Google to do this.
Here is how you can disable the collecting of your phone numbers which is on by default:
Go to Settings -> Google -> All services -> Privacy & security -> Phone number verification. See attached screenshot.
Or even better: switch to #GrapheneOS #LineageOS or other #degoogled systems
Please boost and spread with your not-so-techie friends that might be using stock Google phones
EDIT: corrected typo: it is "all services" not "all devices"
#boost #boost4reach #security #privacy #android
Your #Android phone is in danger ⚡😱
Source: https://www.heise.de/en/news/SMS-of-Death-Security-flaw-crashes-Android-phones-11506625.html
#sms #Software #bug #smartphone #crash #Problem #news #cybersecurity #security
“SMS of Death”: Security flaw crashes Android phones
An invisible text message crashes Android phones, interrupts calls and traps devices in a reboot loop. Google has already responded.Andreas Floemer (heise online)
Wenn es einen nicht bei PHP erwischt, dann bei Node.js 🙄
https://www.aikido.dev/blog/node2shell-nodejs-brotli-rce-cve-2026-111497
Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)
Node.js CVE-2026-111497 (Node2Shell) is a Brotli flaw that can allow remote code execution. See who is affected, patched versions and the fix.Sooraj Shah (Aikido Security)
Say No to UK #ID for online access
Don’t make us show ID to go #online.
Tell #UK Government to:
- Protect #children without making everyone have to provide ID to use everyday websites, apps
- Stop #tech companies using our personal data to target us with harmful ads, content
- Tackle causes of online #harm instead of forcing ID checks
- Support social media models that put people in control
With ID checks, our speech is not #free
https://action.openrightsgroup.org/say-no-id-online-access
Say No to ID for online access
Protect people. Regulate powerful platforms. Keep the internet open. The Government is planning to introduce tough new laws that require all adults to show ID to access to go online. They say this is to keep under 16s off social media.Open Rights Group
LG TV shown scanning LAN for third-party phones and other devices
My TiVo does this too, but, not so comprehensively. Here's some output from iftop.
192.168.1.255:2190 => 192.168.1.2:2190
224.0.0.251:5353 => 192.168.1.2:5353
The broadcast packet on port 2190 is called "TiVo Connect." That's TiVo trying to detect other TiVos on the LAN. The multicast packet on port 5353 is multicast DNS.
https://whatportis.com/ports/2190-tivoconnect-beacon
https://en.wikipedia.org/wiki/Multicast_DNS
#spyware #perversion #privacy #surveillance #liberty #security #spying #unwarranted-investigation #recording #tracking #lg #lg-tv #scanning #lan #tivo
I went looking for surveillance cameras in my neighbourhood: I found so many more than I thought
In the trade-off between #privacy and #security, it helps to know the extent of your local #surveillance infrastructure. There are now easy ways to find out.
https://www.bbc.com/future/article/20260902-how-to-watch-the-cameras-that-watch-you
I went looking for surveillance cameras in my neighbourhood: I found so many more than I thought
In the trade-off between privacy and security, it helps to know the extent of your local surveillance infrastructure. There are now easy ways to find out.Thomas Germain (BBC)
AliExpress was silently running audio in your browser to fingerprint and track your device
#tech #technology #news #technews #security #privacy #aliexpress #fingerprinting
Everything I own, owned - schlarp.com
It's now trivial to turn any USB/WiFi/BT-connected device into a spying device or an attack platform.
https://schlarp.com/posts/everything-i-own-owned/
Everything I own, owned
Turning Claude loose on the firmware of five USB and WiFi peripherals, and finding a command shell in a microphone, a defeatable webcam activity LED, and unauthenticated memory writes over the network.schlarp.com
Digitale Selbstverteidigung muss nicht kompliziert sein. In der Privacy Guide erkläre ich dir, wie du mit wenig Aufwand dein Online Leben deutlich spurenarmer gestalten kannst:
https://gnulinux.ch/privacy-guide
https://fediserve.de/preview.php?v=vimZj8HW0Kg
#privacy #security #sicherheit #firefox #linux #llcoolj #diday


Have you ever tried to build Tails from source?
Tails is a funny sidequest that leads to a whole different set of problems. in line with the theme of this thread of "trusting nothing", have you ever tried to build Tails from source? just to see how it works, and what happens.
you should try it.
hint: the Tails build process is actually broken. nobody has been able to build it for years. when you go through it, you discover it is a hideous patchwork of very insecure programming languages, tools, 3rd party modules. i tried to build Tails and failed. after i saw all the Ruby dependencies it uses, i was horrified because there is no way to keep all of that infrastructure secure from the NSA. Tails is a giant psyop. it's all backdoored. we don't actually know who is building Tails and releasing the binaries. we just have to Trust in Trust that they are not compromised.
Brave is charging $60 to remove features it added in the first place
Another reason to avoid using brave.
https://www.xda-developers.com/brave-is-charging-60-to-remove-features-it-added-in-the-first-place/
#news #tech #technology #socialmedia #twitter #mastodon #bluesky #security #privacy
Brave is charging $60 to remove features it added in the first place
Pay more to get less.Simon Batt (XDA)
Behörde für abgesicherte Ausweise geknackt – Millionen Franzosen betroffen
Frankreichs Behörde für Ausweise gesteht ein, dass Daten von 12 Millionen Franzosen auf dem Schwarzmarkt feilgeboten werden. Der Täter spricht von 19 Millionen.
#Datensicherheit #elektronischerPersonalausweis #IT #Security #Journal #news
Warten auf Sicherheitsupdate: Angreifer attackieren Adobe Reader
Angreifer nutzen derzeit eine Zero-Day-Lücke in Adobe Reader aus. Bis es ein Sicherheitsupdate gibt, sollte man keine PDFs aus unbekannten Quellen öffnen.
#AdobeReader #Cyberangriff #IT #Patchday #Security #Sicherheitslücken #Updates #Exploit #news
Firefox's AI Kill Switch is a Trap: How Mozilla Made AI Your Problem
"Mozilla recently released AI controls for Firefox. On the surface, this sounds like a win for user choice in an era of AI-everything.
If we dig deeper, you can start to see that the kill switch isn’t the whole story. This feature acts like an accountability sink…"
#mozilla #firefox #tech #technology #info #BigTech #browser #internet #safety #security #InfoSec #AI #ArtificialIntelligence #Fuck_AI
Firefox’s AI Kill Switch is a Trap: How Mozilla Made AI Your Problem
TL;DR: Mozilla recently released AI controls for Firefox: a single control panel that lets people disable AI features in the browser or pick and choose which to leave on.Youssuff Quips
Notepad++'s update servers have been compromised by Chinese hackers and all users had been exposed to malware. The developer estimated the overall compromise period spanned from June through December 2, 2025.
Users should update to version 8.9.1 (or superior) immediately.
Source: https://notepad-plus-plus.org/news/hijacked-incident-info-update/
#security #vulnerability #windows #text #editor #notepad #foss #freesoftware #software
Extending Kernel Race Windows Using '/dev/shm'
Recently, I came across this kernelCTF submission where the author mentions a novel technique for extending race windows in the Linux kernel: I learned…faith2dxy.xyz
Something that’s been bothering me for years in the security world: why do researchers demand bug bounties for vulnerabilities in open source projects, when the very contributors maintaining and fixing those issues get nothing, just goodwill?
It feels deeply unfair. The burden falls on unpaid maintainers, yet bounty hunters get rewarded. If you want a paid bounty, maybe help fund the people who actually fix the mess too.
GrapheneOS version 2025061000 released:
https://grapheneos.org/releases#2025061000
See the linked release notes for a summary of the improvements over the previous release.
Forum discussion thread:
https://discuss.grapheneos.org/d/23046-grapheneos-version-2025061000-released
#GrapheneOS #privacy #security
GrapheneOS releases
Official releases of GrapheneOS, a security and privacy focused mobile OS with Android app compatibility.GrapheneOS
**Backdoor Campaign Affecting Thousands of ASUS Routers**
https://www.greynoise.io/blog/stealthy-backdoor-campaign-affecting-asus-routers
**#asus #security #backdoor #malware**
GreyNoise Discovers Stealthy Backdoor Campaign Affecting Thousands of ASUS Routers
GreyNoise uncovers a stealth campaign exploiting ASUS routers, enabling persistent backdoor access via CVE-2023-39780 and unpatched techniques.www.greynoise.io
PSA: The Tor Browser Security Level slider cannot be relied upon without a full browser restart (per an anonymous community report and confirmed by Privacy Guides staff) - Make sure you are aware of this if you rely on this feature for your safety.
https://www.privacyguides.org/articles/2025/05/02/tor-security-slider-flaw/
#TorBrowser #Security #MullvadBrowser #Privacy #PrivacyGuides #Article
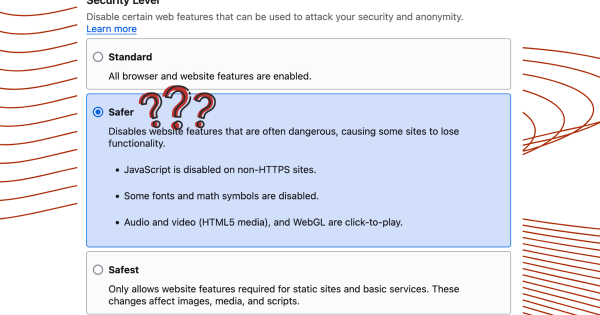
A Flaw With the Security Level Slider in Tor Browser
PSA: The security level slider in Tor Browser (and Mullvad Browser) does not fully apply until restarting the browser.www.privacyguides.org
New Privacy Guides video 📺✨
by @jw
If you've wondered about
the difference between:
Privacy,
Security,
and Anonymity 
And why some privacy-focused
services are worth using even when they don't provide perfect anonymity, watch this!
It's truly an amazing short video!
Everyone should watch it 👇
https://www.privacyguides.org/videos/2025/03/14/stop-confusing-privacy-anonymity-and-security/
#PrivacyGuides #Privacy #Security #Anonymity
Stop Confusing Privacy, Anonymity, and Security
Are you mixing up privacy, security, and anonymity? Don't worry, it's more common than you might think! In this week's video we break down each term, so you can make educated decisions on what tools are best for you.www.privacyguides.org
FreeTube ─ Watch YouTube without ads, without login, and with private playlists.
#google #YouTube #privacy #ad #safety #security #InfoSec #data #advertisement #tech #technology #BigTech #app #apps #tip #tips
FreeTube - The Private YouTube Client
FreeTube is a feature-rich and user-friendly YouTube client with a focus on privacy.freetubeapp.io
https://frederikbraun.de/home-assistant-can-not-be-secured-for-internet-access.html
https://thecopenhagenbook.com/
🔴 Agenda na #JesienLinuksowa już dostępna! 🔴
W programie: #DevOps, #security, #gaming, #prywatność i więcej!
Goście specjalni: Kuba Mrugalski (@uwteam), Tomasz Zieliński (@infzakladowy)
Dodatkowo: 💬 Unconference ⚡ Lightning Talks 🎉 Fedora release party!
Do zobaczenia! 🥳
Do you want to help make software safer? Find the bugs in our ntpd-rs!
The ntpd-rs Bug Bounty Program offers a reward to anyone who finds a qualifying vulnerability.
Read the details here: https://yeswehack.com/programs/pendulum-bug-bounty-program
This Bug Bounty Program is organized and funded by @sovtechfund . Read more about this initiative here: https://www.sovereigntechfund.de/programs/bug-resilience/
ntpd-rs Bug Bounty Program bug bounty program - YesWeHack
ntpd-rs Bug Bounty Program bug bounty program detailsYesWeHack #1 Bug Bounty Platform in Europe
So now that we all understand that thanklessly relying on free work of overworked maintainers is a problem, how about we put our money where our mouth is?
I think @AndresFreundTec needs a fat bonus check for saving our asses.
And Lasse Collin needs a lot of support, and probably a nice vacation.
I pledge $100, for starters.
Now how can we make sure to send the funds to the correct people?
Or is there already any fundraiser that I missed?
„GitHub Disables The XZ Repository Following Today's Malicious Disclosure“
https://www.phoronix.com/news/GitHub-Disables-XZ-Repo
GitHub Disables The XZ Repository Following Today's Malicious Disclosure
Today's disclosure of XZ upstream release packages containing malicious code to compromise remote SSH access has certainly been an Easter weekend surprise..www.phoronix.com
Millions Of #google #whatsapp #Facebook #2FA #Security Codes #Leak Online
Security experts advise against using SMS messages for two-factor authentication codes due to their vulnerability to interception or compromise. Recently, a security researcher discovered an unsecured database on the internet containing millions of such codes, which could be easily accessed by anyone.
#news #tech #technews #technology #privacy
Millions Of Google, WhatsApp, Facebook 2FA Security Codes Leak Online
A security researcher has discovered an unsecured database on the internet containing millions of two-factor authentication security codes. Here's what you need to know.Davey Winder (Forbes)