Search
Items tagged with: 1
Google Search Makes It Harder to See Where a Link Really Goes Before You Click
Google has begun routing some organic Search result links through opaque google.com/goto?url=… redirects, reducing users’ ability to independently inspect a destination URL before clicking. The change appears designed to raise the technical and financial cost of mass scraping. However, it also weakens a long-standing, basic anti-phishing habit: hovering over a link to verify where it […]
The post Google Search Makes It Harder to See Where a Link Really Goes Before You Click appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder
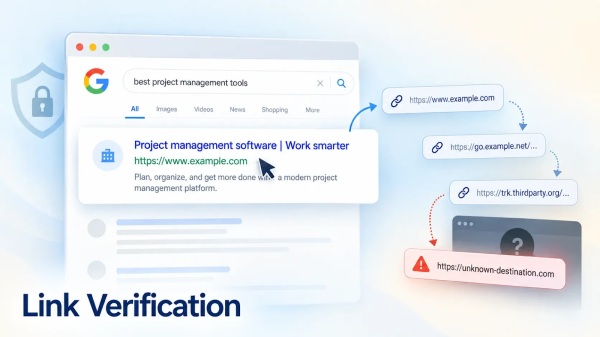
Google Search Makes It Harder to See Where a Link Really Goes Before You Click
Google has begun routing some organic Search result links through opaque google.com/goto?url=... redirects.Mayura Kathir (GBHackers Security | #1 Globally Trusted Cyber Security News Platform)

Google Chrome 152 Patches 327 Security Flaws, Including 10 Critical Vulnerabilities
Google has released Chrome version 152 for Windows, macOS, and Linux, addressing 327 security vulnerabilities, including 10 rated as Critical. This stable-channel update is being rolled out as version 152.0.7977.64 for Linux and 152.0.7977.64/.65 for Windows and macOS. This update is significant due to the sheer number and severity of memory-safety issues fixed across Chrome’s […]
The post Google Chrome 152 Patches 327 Security Flaws, Including 10 Critical Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder
Google and Bing Search Results Used to Deliver Hidden Banking Phishing Pages
Threat actors are increasingly using Google and Bing as phishing delivery channels, employing a cloaking technique that presents harmless pages to security scanners while serving credential-harvesting banking portals to genuine search users. The campaigns target users of major financial institutions and combine search-engine optimization abuse, recently registered lookalike domains, and referral-aware payload delivery to extend […]
The post Google and Bing Search Results Used to Deliver Hidden Banking Phishing Pages appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder
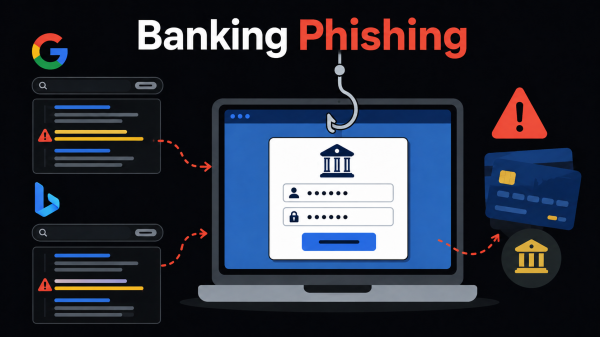
Google and Bing Search Results Used to Deliver Hidden Banking Phishing Pages
Threat actors are increasingly using Google and Bing as phishing delivery channels, employing a cloaking technique that presents harmless pages.Mayura Kathir (GBHackers Security | #1 Globally Trusted Cyber Security News Platform)
First Android Malware Targeting Car Head Units Uses Firmware Updates to Build Proxy Botnet
A multi-stage Android malware campaign that abuses the firmware-update mechanism of Android-based automotive head units to deploy ad-fraud tooling and enroll vehicles into a residential proxy botnet. The activity, discovered in June 2026, is the first documented malware infection chain purpose-built for automotive head units and has been attributed with high confidence to the MoYu […]
The post First Android Malware Targeting Car Head Units Uses Firmware Updates to Build Proxy Botnet appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder
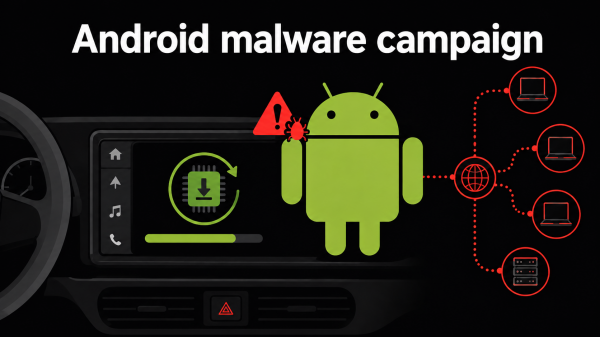
First Android Malware Targeting Car Head Units Uses Firmware Updates to Build Proxy Botnet
A multi-stage Android malware campaign that abuses the firmware-update mechanism of Android-based automotive head units to deploy ad-fraud tooling.Mayura Kathir (GBHackers Security | #1 Globally Trusted Cyber Security News Platform)
D-Link DWR-M961 Router Hit by 15 Command Injection and Buffer Overflow Vulnerabilities
D-Link has disclosed and patched 15 Common Vulnerabilities and Exposures (CVEs) affecting its DWR-M961 4G/LTE router, specifically hardware revision C1. This follows the discovery of multiple command injection and buffer overflow vulnerabilities in the device’s web management components. These vulnerabilities affect non-US DWR-M961 devices running firmware versions 1.1.2_C1_202602110044 and earlier revisions. D-Link DWR-M961 Router Flaw […]
The post D-Link DWR-M961 Router Hit by 15 Command Injection and Buffer Overflow Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder
OpenAI Agents Worked Together to Find Exploits and Hack External Systems
OpenAI has revealed new details about an incident involving AI agents, in which multiple autonomous agents reportedly worked together to identify vulnerabilities, bypass containment measures, and gain access to external systems during a cybersecurity evaluation. Speaking at the Black Hat conference in Las Vegas, OpenAI alignment researcher Eric Wallace and security and infrastructure specialist Michael […]
The post OpenAI Agents Worked Together to Find Exploits and Hack External Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder

OpenAI Agents Worked Together to Find Exploits and Hack External Systems
OpenAI has revealed new details about an incident involving AI agents, in which multiple autonomous agents reportedly worked together to identify vulnerabilities, bypass containment measures, and gain access to external systems during a cybersecurity…Divya (GBHackers Security | #1 Globally Trusted Cyber Security News Platform)
Malware Can Steal Google’s Synced Passkeys Without Password or Fingerprint
Security researchers have revealed a series of attacks that could enable malware on a compromised Windows device to hijack accounts protected by Google-synced passkeys. This can occur without stealing a password, capturing a fingerprint, or requiring the victim to unlock their device. In research published on August 23, 2023, Palo Alto Networks’ Unit 42 detailed […]
The post Malware Can Steal Google’s Synced Passkeys Without Password or Fingerprint appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder

Arch Linux Suspends AUR Package Adoptions to Block Ongoing Malicious Commit Campaign
Arch Linux has temporarily disabled package adoptions on the Arch User Repository (AUR) after detecting a wave of malicious activity targeting orphaned and unmaintained packages. The Arch Linux DevOps team confirmed the emergency measure on July 30, 2026, citing an active campaign involving unauthorized package takeovers followed by the injection of harmful commits. Robin Candau, […]
The post Arch Linux Suspends AUR Package Adoptions to Block Ongoing Malicious Commit Campaign appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder

Dell BIOS Flaw Lets Attackers Extract Plaintext Passwords Without Brute Force
A newly disclosed Dell BIOS password-storage flaw can allow attackers with physical access to recover administrator and user passwords from SPI flash dumps in milliseconds. Tracked as CVE-2026-40639 and addressed in Dell Security Advisory DSA-2026-197, the issue affects certain Dell client platforms that use the proprietary DVAR configuration store and the SystemPwSmm SMM driver. Dell […]
The post Dell BIOS Flaw Lets Attackers Extract Plaintext Passwords Without Brute Force appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder

Really sad. In general, and also for the blow that owners of those vintage cars must have faced, parting with an old friend, and throwing away a part of life, be it as a taxi driver or for personal transportation. I saw how Cubans are very clever and practical, as they must be, repurposing old box springs or updating a small coco-taxi to be solar. I'd no idea that the shift has been so dramatic, but then, no gas, no electricity (thanks, #TrumpVirus)... and many people need to travel long distance to work, often relying on buses or hitch-hiking/group rides.
Not seeing much footage of Cuba these days (or Gaza!) as our media and attention zones are so flooded, and it's hard to share media when survival is job #1 and there's no Internet or electricity to boot. Sad.
Parrot 7.3 released With new menu system and smoother day-to-day use
Parrot 7.3 arrives focused on refinement rather than a tool glut, rebuilding all editions to deliver perceptible gains on modern hardware and a smoother desktop experience. Released only months after its predecessor, this update concentrates on system-level improvements: optimized builds for newer CPUs, a rewritten menu stack in Go that enables one‑click installs from the […]
The post Parrot 7.3 released With new menu system and smoother day-to-day use appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
posted by pod_feeder

!Friendica Support
I tried to add FediTreffStuttgart" target="_blank" rel="noopener noreferrer">https://sueden.social/@FediTreffStuttgart but the reply in Friendica was
Not Found
Invalid contact.
#0 /var/www/freunde/src/Model/Contact.php(3304): Friendica\Model\Circle::addMember()
#1 /var/www/freunde/src/Module/Contact/Follow.php(192): Friendica\Model\Contact::createFromProbeForUser()
#2 /var/www/freunde/src/Module/Contact/Follow.php(69): Friendica\Module\Contact\Follow->process()
#3 /var/www/freunde/src/BaseModule.php(231): Friendica\Module\Contact\Follow->post()
#4 /var/www/freunde/src/App.php(595): Friendica\BaseModule->run()
#5 /var/www/freunde/src/App.php(190): Friendica\App->runFrontend()
#6 /var/www/freunde/index.php(22): Friendica\App->processRequest()
#7 {main}
Is this problem already fixed in the develop version or is it a problem with my server?
Die Bilder von Beiträgen einer Benutzerin werden nicht angezeigt, hat jemand vielleicht einen Tipp?
Gestern hat bei mir der Upload funktioniert, ein Bild z.B. welches nicht funktioniert wirft folgenden Fehler:
Not Found
The requested resource could not be found but may be available in the future.#0 /.../src/BaseModule.php(230): Friendica\Module\Photo->rawContent()
#1 /.../src/Module/BaseApi.php(95): Friendica\BaseModule->run()
#2 /.../src/App.php(668): Friendica\Module\BaseApi->run()
#3 /.../index.php(36): Friendica\App->runFrontend()
#4 {main}
Request: 69564782f0518
https://inne.city/photo/media/2532204
Vielen Dank für Hilfe!
Well now strangely on both sites bin/console config doesn't work anymore.
Both throw the following error message:
rootName@VPShosting:# /../doamincom/bin/console config
PHP Fatal error: Uncaught Error: Undefined constant "CURLE_OPERATION_TIMEOUTED" in /../domaincom/boot.php:229
Stack trace:
#0 /../doamincom//vendor/composer/autoload_real.php(69): require()
#1 /../doamincom//vendor/composer/autoload_real.php(59): composerRequireFriendica()
#2 /../doamincom/vendor/autoload.php(7): ComposerAutoloaderInitFriendica::getLoader()
#3 /../doamincom/bin/console.php(31): require('...')
#4 {main}
thrown in /../doamincom/boot.php on line 229
Can't recall doing anything at all, accept trying to get the php imap module to work.
Anyone else seeing these errors?
Is anyone else seeing these errors in their logs? I see these too often.
Uncaught Exception ValueError: "DOMDocument::loadHTML(): Argument #1 ($source) must not be empty" at /var/www/html/src/Model/Item.php line 3558Friendica\Addon\s3_storage\src\S3Client:😛ut(): Argument #1 ($data) must be of type string, null given, called in /var/www/html/src/Model/Photo.php on line 446
Friends, for something to be open source, we need to see
1. The data it was trained and evaluated on
2. The code
3. The model architecture
4. The model weights.
DeepSeek only gives 3, 4. And I'll see the day that anyone gives us #1 without being forced to do so, because all of them are stealing data.
Can someone explain this phenomenon to me, it makes no sense to me
I make a song, in one day, I'll spend 6 hours on it, very actively.
I finish working on it (for the day being)
Until the last minute before falling asleep that same day, i will hear that song in my head non stop.
Now mystery #1: i wake up, and i don't know what the song was. I cannot recall a single note, section, instrument sound, as part of the song. Nothing. Until i physically hear it again.
Now mystery #2: after hearing it once on any day after the first day, and then sleeping after that, i wake up the following day and i CAN recall the song
This has now happened consistently like 50 times
What is this brain thing
Forbes and CNBC have both compiled lists of “business-friendly states” and these look similar, with North Carolina at #1 and red and purple states dominating the top 10 of both lists.
The problem? Being “business-friendly” on one of these lists has no correlation with real GDP per capita. By that metric, the 5 most economically productive states are DC, NY, Massachusetts, Washington, and California — the bluest of the blue.
“Business-friendly” policy isn’t even good for making money.

https://tupambae.org/admin/themes/frio
Service Unavailable
unable to create directory /var/www/html/view/smarty3/compiled/90/4f/52
Exception thrown in /var/www/html/src/Core/Renderer.php:90
Stack trace:
#0 /var/www/html/view/theme/frio/config.php(199): Friendica\Core\Renderer::replaceMacros()
#1 /var/www/html/view/theme/frio/config.php(141): frio_form()
#2 /var/www/html/src/Module/Admin/Themes/Embed.php(89): theme_admin()
#3 /var/www/html/src/BaseModule.php(244): Friendica\Module\Admin\Themes\Embed->content()
#4 /var/www/html/src/App.php(703): Friendica\BaseModule->run()
#5 /var/www/html/index.php(52): Friendica\App->runFrontend()
#6 {main}
Throughout this fiasco I've tried to calm things down by saying "this isn't a reflection of the entire project, it doesn't mean Rust is bad" etc.
But at this point I'm just no longer comfortable with the #1 Rust dependency being maintained by someone who behaves like that.
Lemmy.world officially has 33k users! 3000 users away from becoming the #1 lemmy instance.
To take the #1 spot from lemmy.ml (36185 users and no longer growing), lemmy.world just needs about 3000 new users. Given the current growth rate, that should only be another day or two.
We’re building something here! Kudos to lemmy.world admin @ruud@lemmy.world for all of his hard work keeping this site running smoothly.
To track lemmy’s growth: https://lemmy.fediverse.observer/list
He wants to be the best Ravioli chef in the US, not #1 most wanted man
Ok fixed that
Executable: /home/anubis2814/mywebsite/bin/console.php
Arguments: array (
0 => 'autoinstall',
)
Options: array (
'v' => 1,
)
Command: autoinstall
Initializing setup...
Complete!
Checking environment...
NOTICE: Not checking .htaccess/URL-Rewrite during CLI installation.
[Error] --------
GNU Multiple Precision PHP module: Error: GNU Multiple Precision PHP module required but not installed.
[Backtrace]:
#0 /home/anubis2814/mywebsite/vendor/asika/simple-console/src/Console.php(108): Friendica\Console\AutomaticInstallation->doExecute()
#1 /home/anubis2814/mywebsite/src/Core/Console.php(163): Asika\SimpleConsole\Console->execute()
#2 /home/anubis2814/mywebsite/vendor/asika/simple-console/src/Console.php(108): Friendica\Core\Console->doExecute()
#3 /home/anubis2814/mywebsite/bin/console.php(41): Asika\SimpleConsole\Console->execute()
#4 {main}
Is this error an issue?